

Parameter
- 348 Seiten
- 13 Lesestunden
Mehr zum Buch
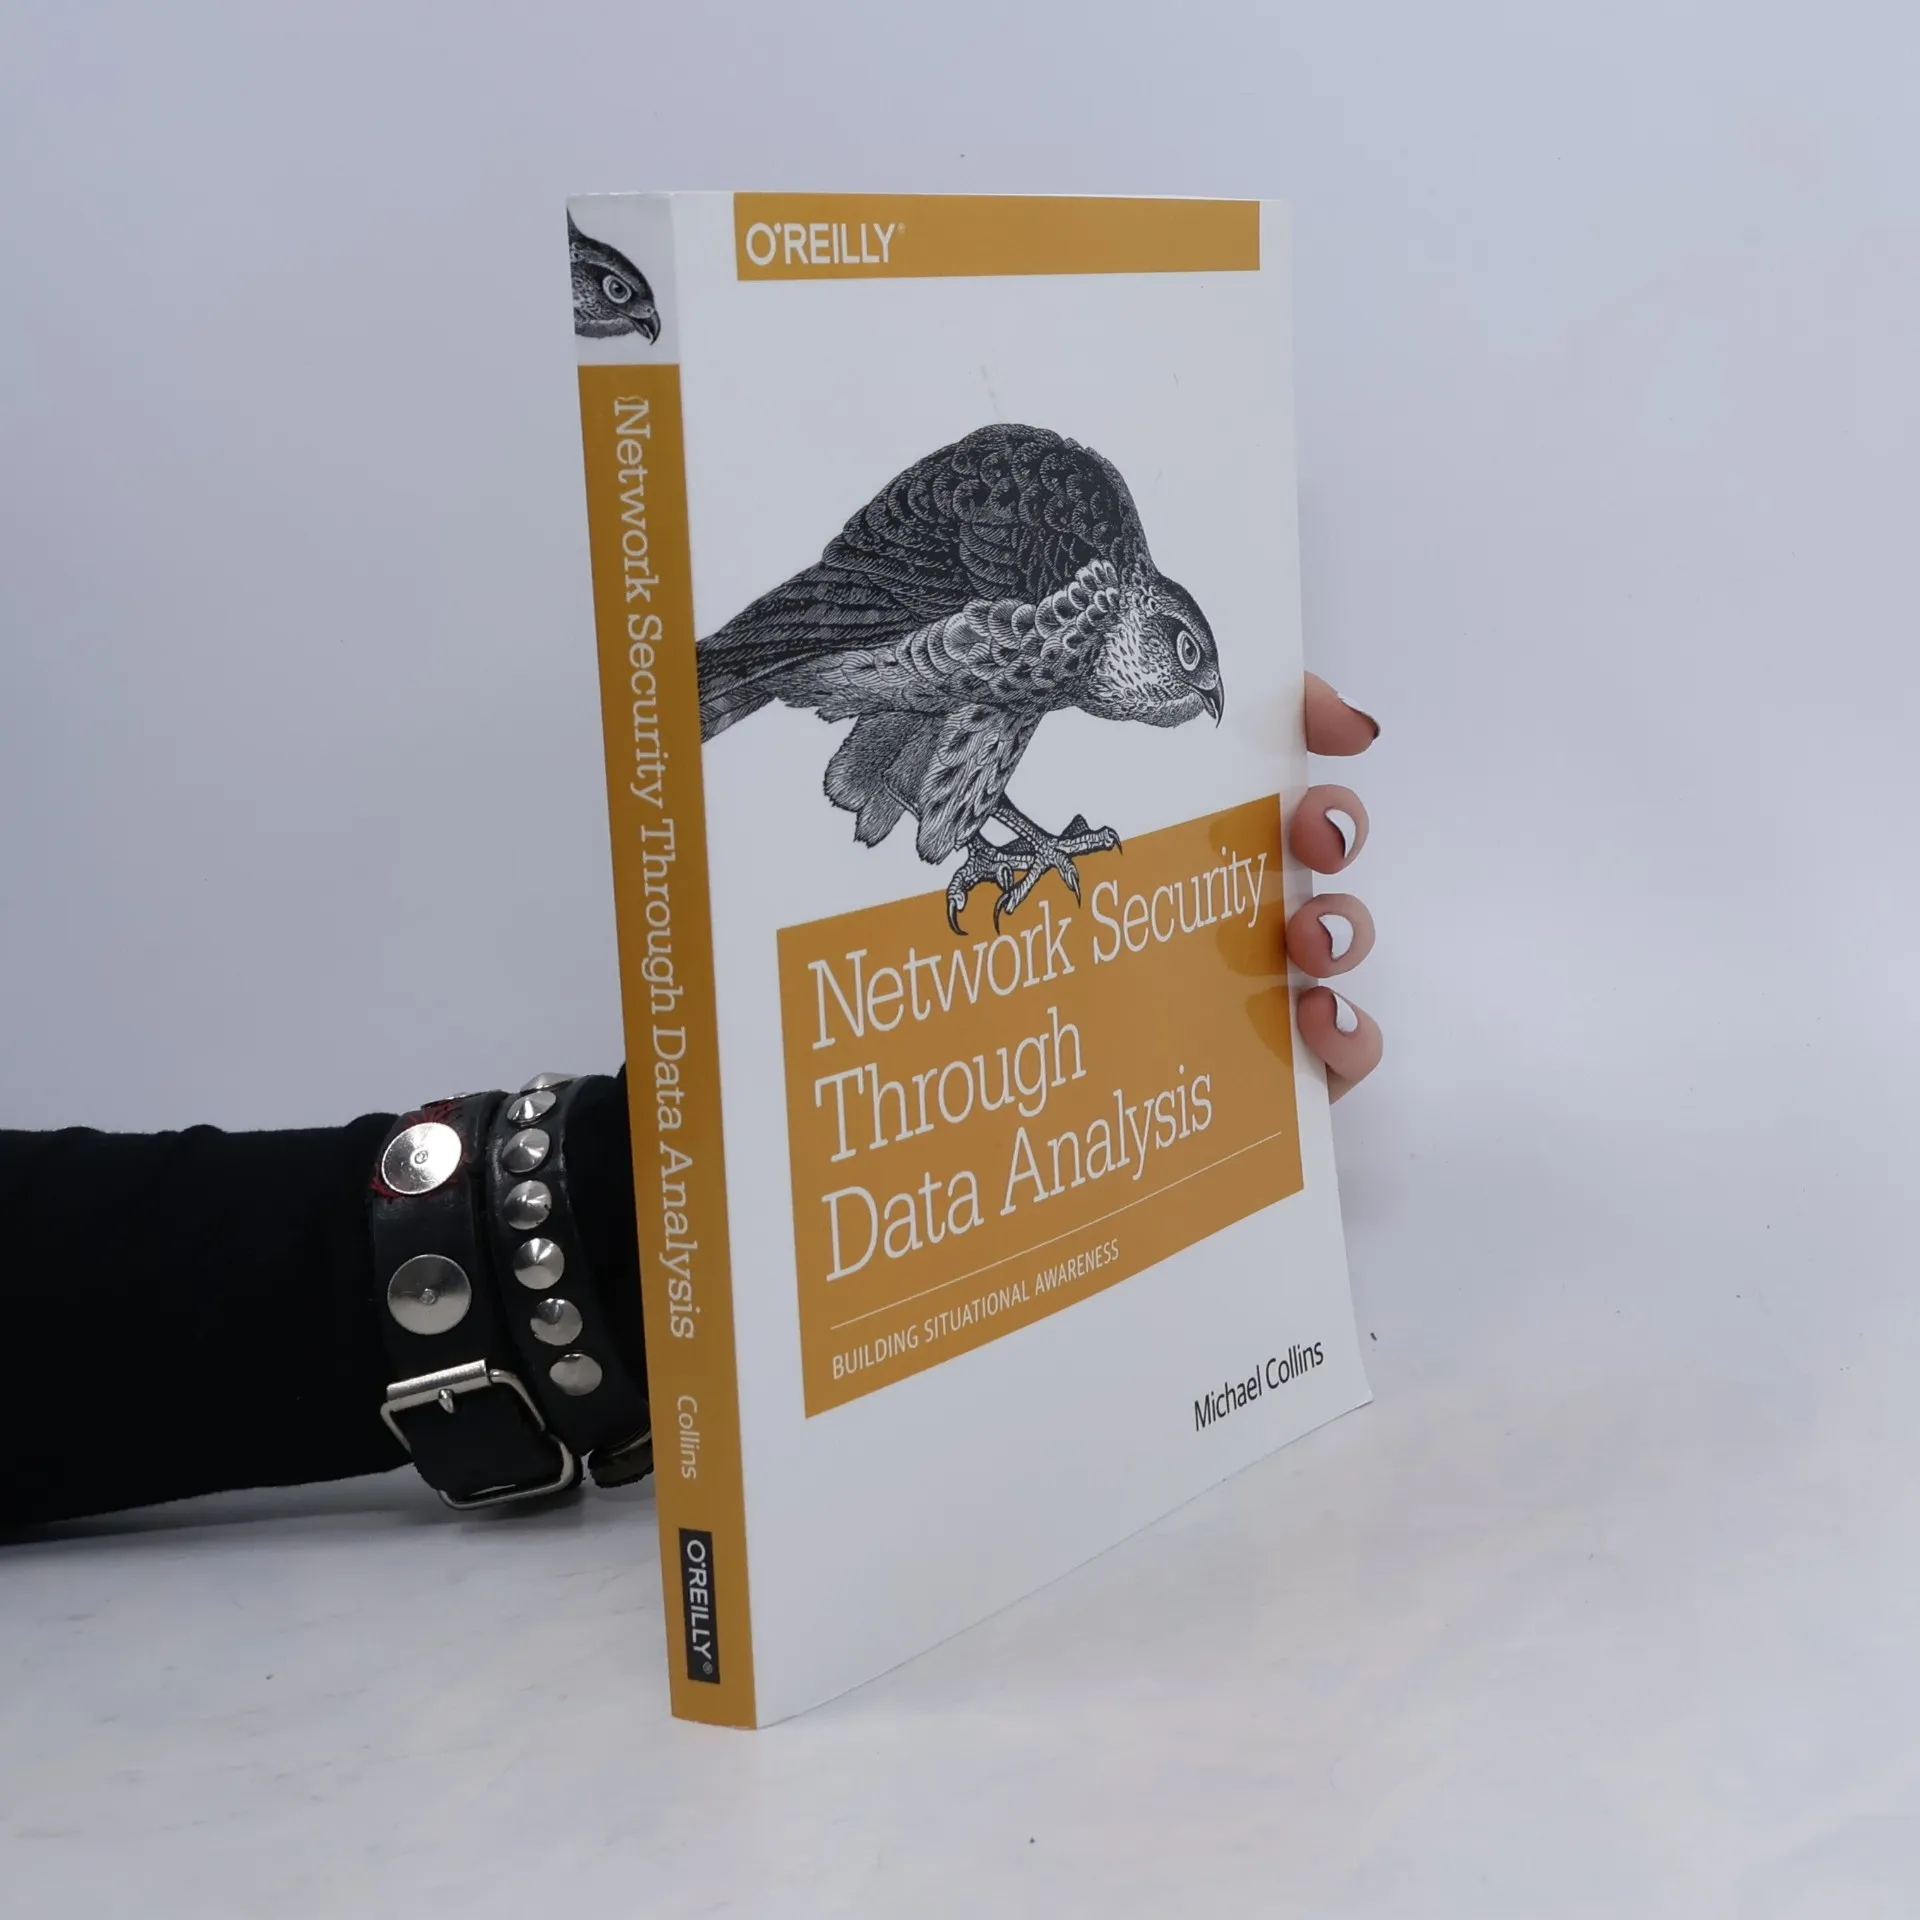
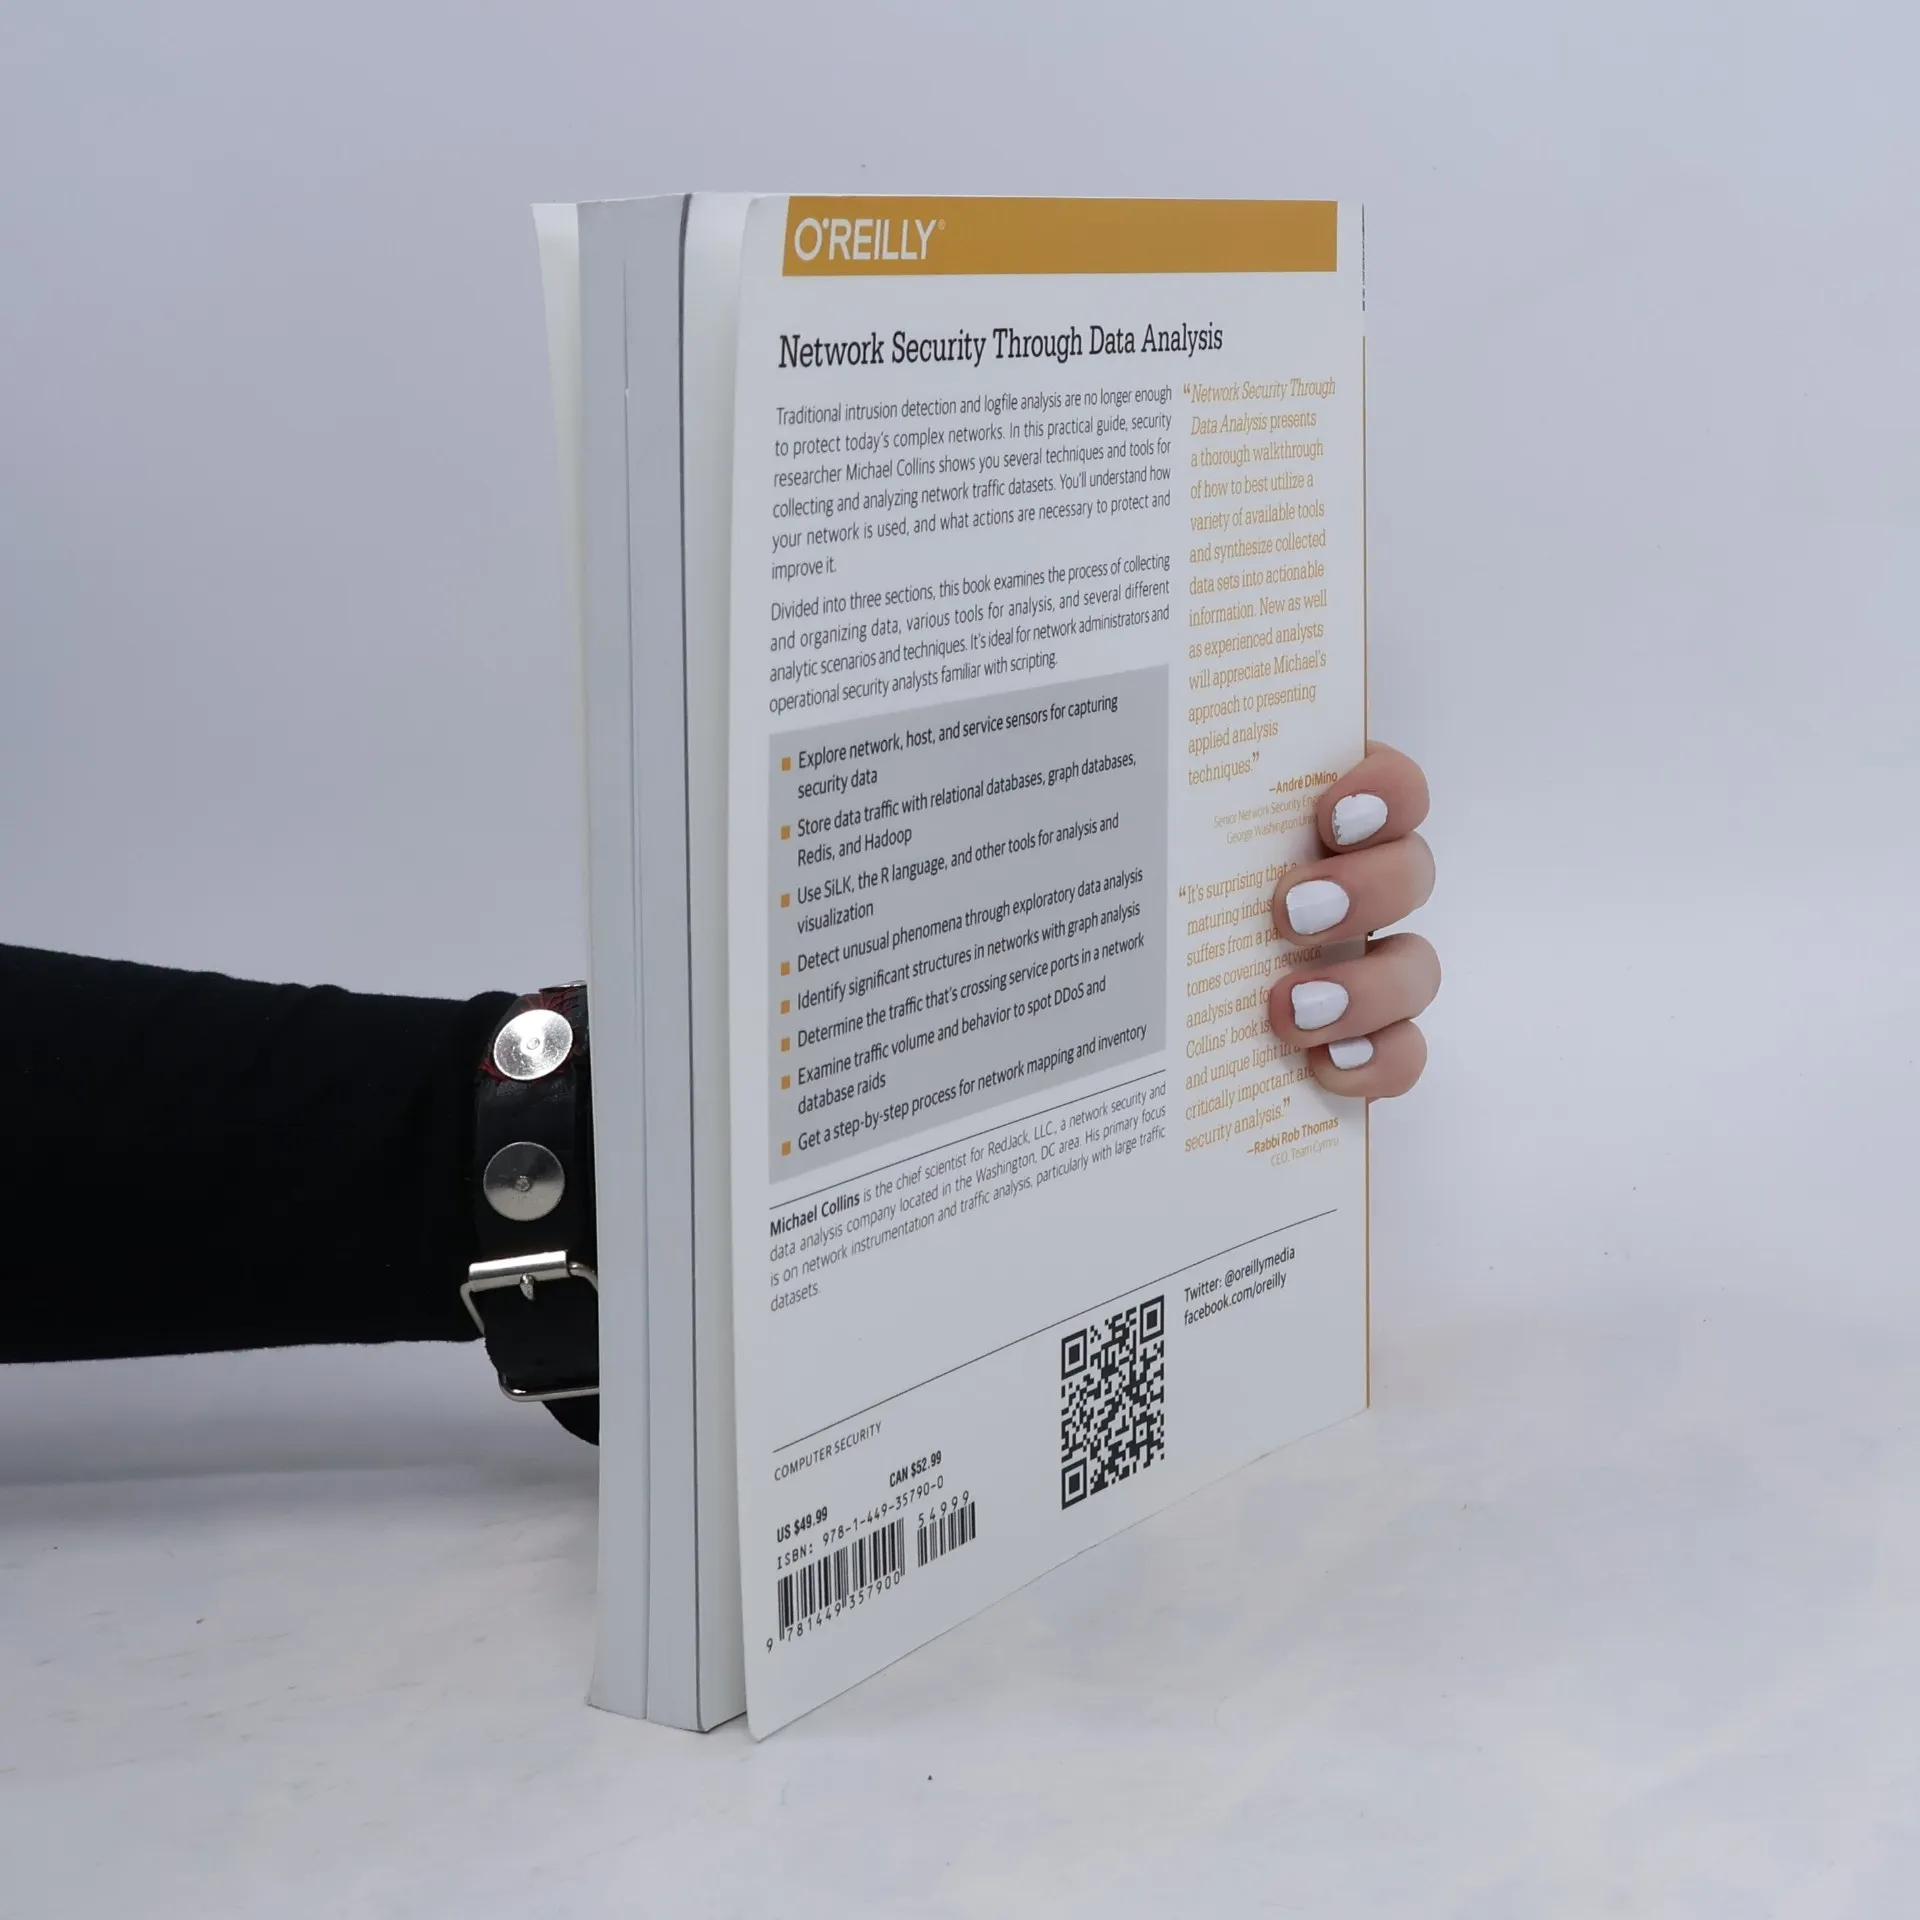
System and network administrators have traditionally monitored their systems through general tools such as intrusion detection and logfile analysis. But modern, complex networks, suffering from more and more sophisticated attacks, deserve more analytical tools. Michael Collins, a leading researcher in security, introduces the techniques needed in this book and highlights some of the computing tools that will help catch problems. The book is divided into three large sections: data collection, analysis, and taking action. These can be iterative, as each discovery alerts the administrator to data that should be collected. Several forms of analysis and visualization are covered. Topics include: What data to capture on your systems Data fusion Structures and storage systems for data Using R, SiLK, and Python for analysis Visualization and exploratory data analysis Graph analysis Network mapping Address forensics: determining where traffic originates Handling malware
Buchkauf
Network Security Through Data Analysis, Edgar Collins
- Sprache

- Erscheinungsdatum
- 2014
- Einband
- (Paperback),
- Buchzustand
- Gebraucht - Gut
- Preis
- € 15,99
Keiner hat bisher bewertet.
- Titel
- Network Security Through Data Analysis
- Untertitel
- Building Situational Awareness
- Sprache
- Englisch
- Autor*innen
- Edgar Collins
- Verlag
- O'Reilly Media
- Erscheinungsdatum
- 2014
- Einband
- Paperback
- Seitenzahl
- 348
- ISBN10
- 1449357903
- ISBN13
- 9781449357900
- Reihe
- Schlagwörter
- Handbücher und Anleitungen, USA, Technologie, Fachliteratur, Kommunikation, Sicherheit, Datenanalyse, Computernetzwerke, Big Data, Visualisierung, Seide
- Beschreibung
- System and network administrators have traditionally monitored their systems through general tools such as intrusion detection and logfile analysis. But modern, complex networks, suffering from more and more sophisticated attacks, deserve more analytical tools. Michael Collins, a leading researcher in security, introduces the techniques needed in this book and highlights some of the computing tools that will help catch problems. The book is divided into three large sections: data collection, analysis, and taking action. These can be iterative, as each discovery alerts the administrator to data that should be collected. Several forms of analysis and visualization are covered. Topics include: What data to capture on your systems Data fusion Structures and storage systems for data Using R, SiLK, and Python for analysis Visualization and exploratory data analysis Graph analysis Network mapping Address forensics: determining where traffic originates Handling malware